Beyond MTTD and MTTR: How to Prove the Business Value of an AI-Enabled SOC
Publish Date: October 9, 2026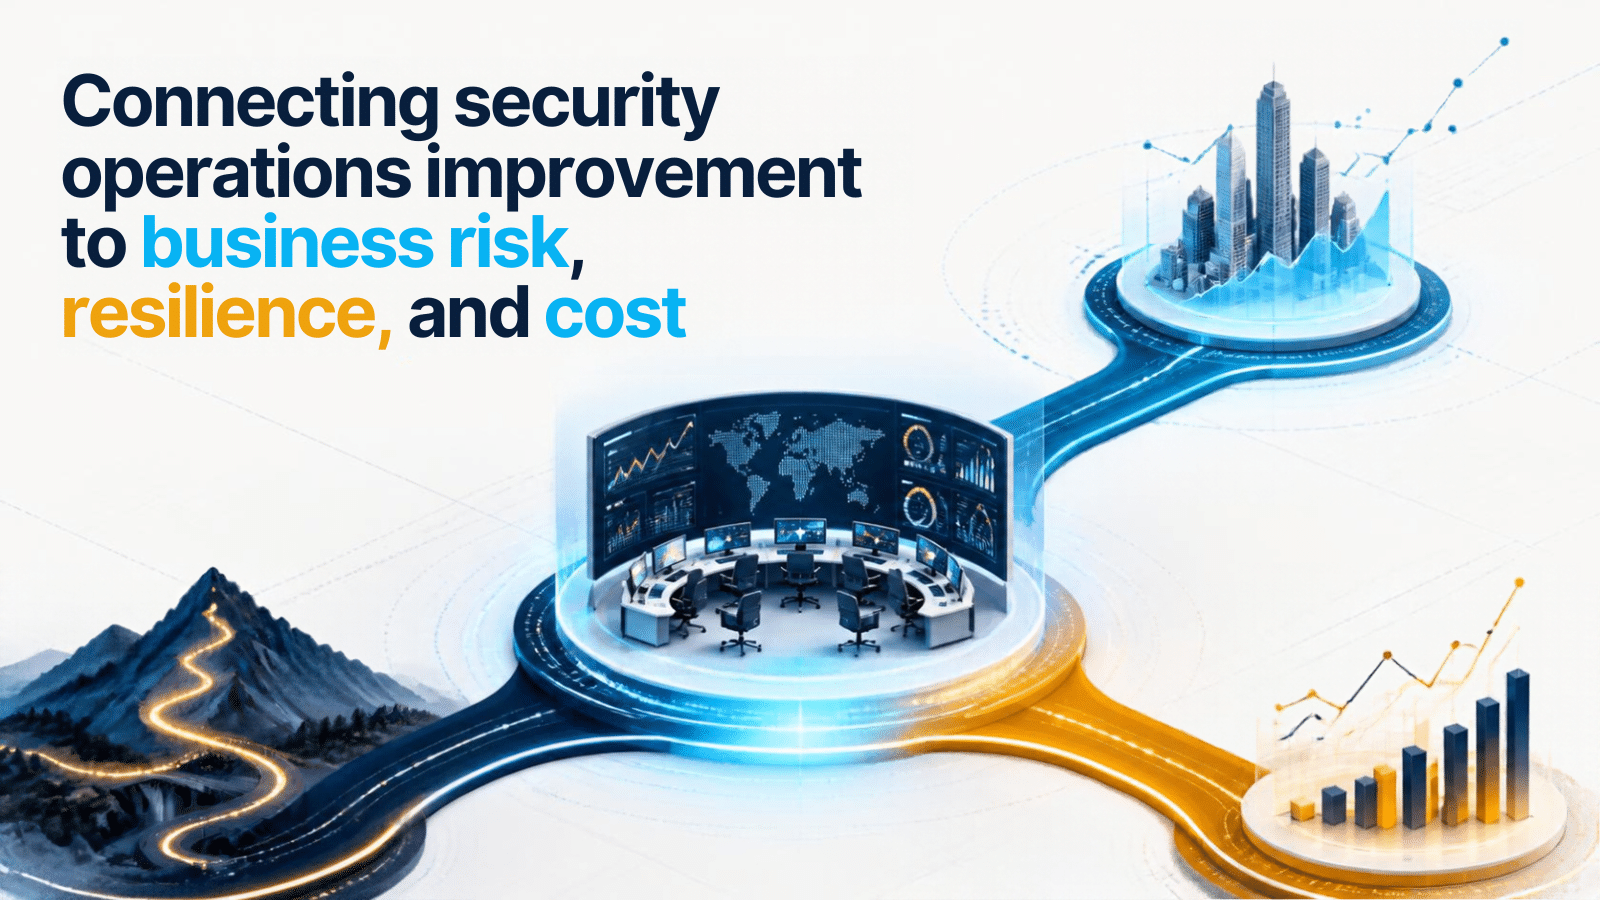
The business case for an AI-enabled SOC often begins with efficiency. Analysts spend less time gathering evidence, investigations move faster, and repetitive tasks are automated. Leadership will still ask a more important question: What changed for the business?
A credible answer must go beyond hours saved or alerts closed. It should show whether the organization understands incidents sooner, contains material threats faster, protects critical operations more consistently, and manages the capability at a predictable cost.
Start with outcomes, not activity
Productivity is valuable when reclaimed capacity produces a clear result. That may mean investigating more incidents to conclusion, improving escalation quality, expanding proactive work, or absorbing growth in security signals without a proportional increase in workload.
Make that conversion visible. Instead of reporting that AI saved analyst time, show how the capacity was used and what improved as a result.
Build the baseline before the pilot
Value is difficult to prove without a reliable starting point. Before introducing AI into a priority workflow, capture how the current process performs.
Useful baseline measures include time to understand scope, time to reach a validated decision, time to contain the threat, analyst effort per case, escalation quality, reopened incidents, false containment actions, and disruption caused by response activities.
Segment the results by incident type and severity. A single average can hide where the SOC is improving and where material risk remains unchanged.
Connect every AI use case to a testable result
Each AI capability should have a clear outcome hypothesis. Automated enrichment should shorten the path to a decision. Entity correlation should improve the quality of escalations. Case summarization should reduce information loss during handovers. Controlled response actions should reduce the period between detection and containment.
Write the expected result before the pilot and compare it with actual performance. If the outcome does not improve, leaders can refine, pause, or decline to scale the capability.
Translate SOC improvement into business language
Metrics such as MTTD and MTTR remain useful inside the SOC, but executives need to understand what those improvements mean for the organization.
One useful translation is exposure duration: how long a material threat had access before it was understood and contained. Reducing that window can limit the opportunity for lateral movement, privilege escalation, data exposure, operational disruption,.
The same principle applies to business services. Show whether the SOC identified the affected service and sensitive data sooner, enabled faster decisions, and reduced the chance that response actions would interrupt critical operations.
Put value, cost, and control in one view
An AI SOC scorecard should not show benefits in isolation. Track operating costs such as licensing, data consumption, integration, testing, and oversight alongside the outcomes being delivered.
Control indicators also matter. These may include analyst override rates, failed automations, open exceptions, false containment events, and operational disruption caused by automated actions. A capability that is difficult to control, expensive to scale, or disruptive is not delivering sustainable value.
Create an executive scorecard that builds trust
A concise scorecard should give leaders a balanced view across six areas:
- Risk outcomes: exposure duration and material incidents contained.
- Operational performance: decision speed, containment speed, and escalation quality.
- Workforce impact: capacity redirected to higher-value security work.
- Control effectiveness: overrides, exceptions, failed actions, and disruption.
- Adoption: where AI is being used and whether the intended workflows are benefiting.
- Cost: current spend, consumption trends, and the cost of scaling.
Use stable measures and show trends over time. Report underperformance with the corrective action. Transparent reporting shows that the program is being managed, not simply promoted.
The bottom line
An AI-enabled SOC earns confidence when business value is measurable and the controls behind it are visible. The strongest case is built on evidence collected before, during, and after implementation, not on technology promises alone.
Start with one priority workflow. Define the business outcome, establish the baseline, track benefit, cost, and control together, and scale only when the evidence supports it.
Ready to turn security signals into faster, better-informed business decisions? Explore how YASH’s AI-enabled SOC services can help strengthen security operations, improve resilience, and reduce operational risk – https://www.yash.com/campaign/ai-autonomous-soc-services/
Shivaram Jeyasekaran
Director – Cybersecurity Services, YASH Technologies
A distinguished cybersecurity leader with over 23 years of experience transforming enterprise security landscapes across global organizations. He is recognized for architecting and scaling robust cybersecurity programs that align with business objectives while maintaining cutting-edge defense capabilities. Shivaram has spearheaded numerous large-scale cybersecurity consulting engagements in his illustrious career, helping organizations navigate complex security challenges while balancing innovation with risk management. His approach combines strategic vision with practical implementation, ensuring organizations stay resilient in the face of evolving cyber threats.
More From Author.
Related Posts.
Your SOC Has Enough Alerts. Does It Deliver the Answers the Business Needs?
Shivaram Jeyasekaran
The Future of Security Operations Is Decision Intelligence-Augmented
Senthilvel Kumar
The Microsoft Security Shift CISOs Can’t Ignore
Mahipal Kirupanithy Senthilvel Kumar Shivaram Jeyasekaran
Your SOC Is Using AI. But Who Is Securing the AI Layer?
Shivaram Jeyasekaran
AI vs AI: Why Traditional SOCs Are Losing the 2026 Threat Race
Senthilvel Kumar Vikash Kumar
Mythos Moves in Hours. Your MTTD Starts Too Late
Shivendra Sharma