Cybersecurity as a Deal Maker: Reframing Security Due Diligence as a Growth Enabler
Publish Date: September 24, 2026Imagine discovering a critical cybersecurity vulnerability after a billion-dollar acquisition has already closed. What was expected to be a growth catalyst suddenly becomes a source of regulatory penalties, customer distrust, and integration delays.
For years, cybersecurity due diligence in M&A has been approached primarily as a risk-management exercise. However, in today’s digital economy, cybersecurity is increasingly becoming a strategic differentiator that influences valuation, accelerates integration, strengthens customer trust, and enables innovation.
This paper explores how forward-thinking CIOs, CDOs, and CISOs can transform cybersecurity from a defensive control into a value creation engine throughout the M&A lifecycle.
Introduction: Rethinking Cybersecurity in the M&A Landscape
Mergers and acquisitions (M&A) have long been engines of growth and transformation for businesses. Yet, as digital assets become central to business value, cybersecurity has shifted from a postscript in due diligence to a decisive factor in deal success. For CIOs, CDOs, and CISOs, the conversation can no longer center solely on risk mitigation. Instead, cybersecurity must be reframed as a strategic lever—a deal maker that can accelerate integration, build stakeholder trust, and unlock new avenues for growth. This thought paper explores how security due diligence, when approached proactively, can enhance deal value and set the stage for long-term competitive advantage.
Key Arguments: Cybersecurity as a Growth Enabler in M&A
1. Elevating Deal Value Through Robust Cybersecurity
Traditionally, security due diligence has been viewed as a checklist item—a necessary but uninspiring hurdle to clear before closing. However, recent data highlights a paradigm shift. For example, in a major acquisition, cybersecurity vulnerabilities identified during due diligence led to a $350 million reduction in deal value and revised transaction terms. Deals involving companies with strong security frameworks not only close faster but often command premium valuations.
2. Accelerating IT Integration and Reducing Post-Merger Friction
A unified cybersecurity strategy can dramatically streamline post-merger IT integration. This directly impacts business continuity and customer experience. Recent M&A analyses show that aligning cybersecurity frameworks early can significantly accelerate IT integration and reduce regulatory friction. For example, in a major acquisition, comprehensive cybersecurity assessments conducted before close enabled smoother integration of IT environments and reduced operational disruption.
3. Fostering Trust and Innovation Among Stakeholders
Cybersecurity excellence signals to customers, partners, and regulators that the merged organization is a trustworthy steward of sensitive data. This reputation builds confidence and can open doors to new markets. Moreover, a robust security foundation empowers IT teams to innovate without fear of exposing critical assets.
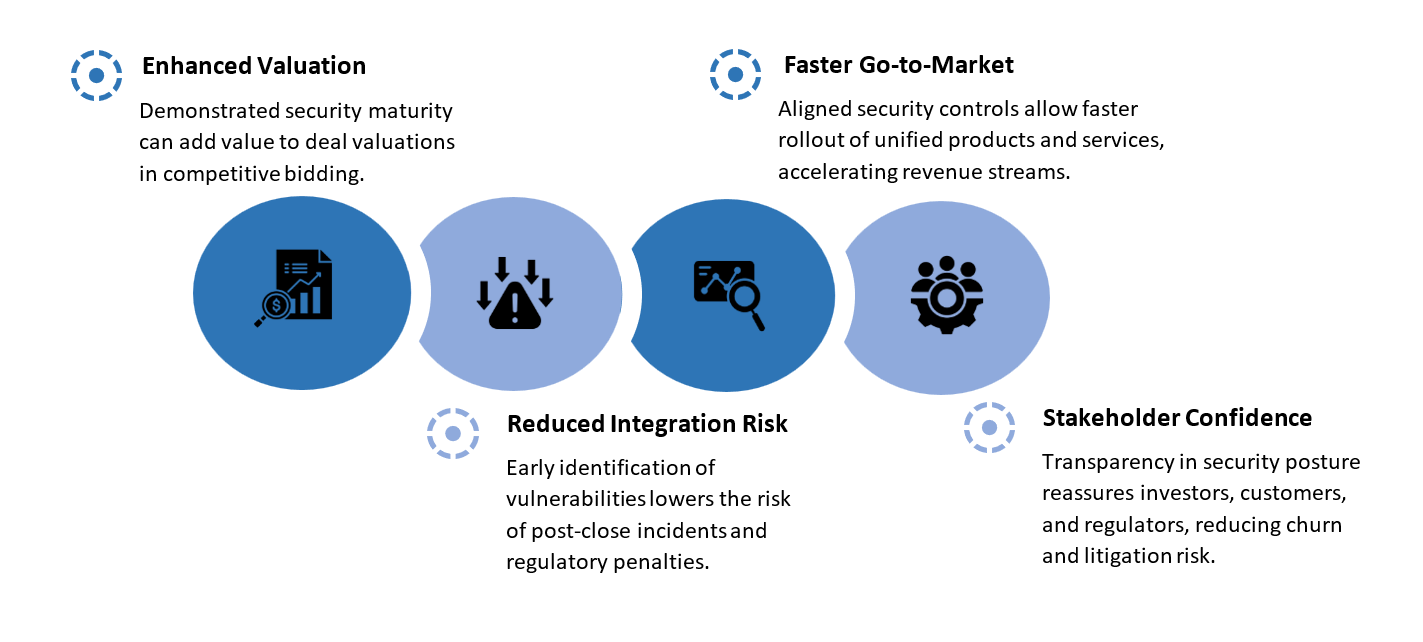
Benefits of Proactive Security Due Diligence
Counterarguments and Practical Responses
“Cybersecurity Due Diligence Is Too Costly and Time-Consuming”
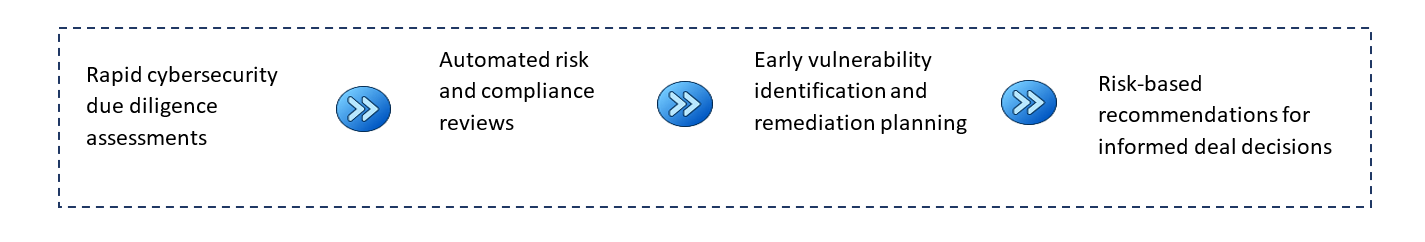
While security assessments do require upfront investment, the cost of post-merger breaches or regulatory fines is exponentially higher. Automated tools, standardized checklists, and third-party assessments can streamline the process, making it both affordable and effective. For example, a large hospitality merger inherited a data breach that affected 383 million customer records, resulting in regulatory fines and substantial remediation costs.
How YASH can help
“Security Integration Is Too Complex Across Different Cultures and Systems”
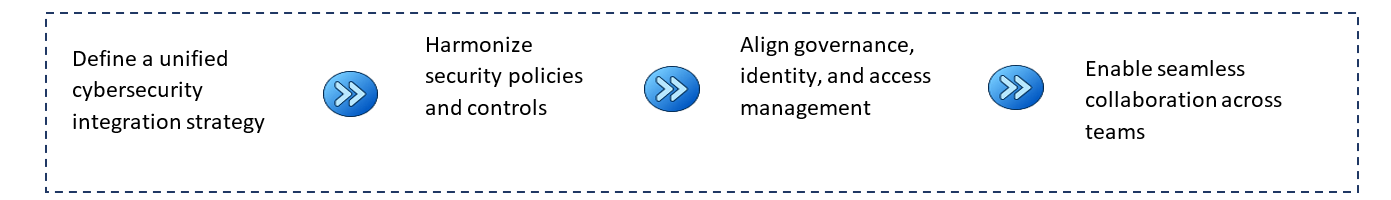
Cultural and technical differences are real, but they are surmountable with the right approach. Establishing joint integration teams, adopting shared security frameworks, and conducting regular cross-functional workshops can bridge gaps. The key is to treat security integration as a core workstream—on par with financial and operational alignment—rather than an afterthought.
How YASH can help
“Cybersecurity Can Slow Down Innovation”
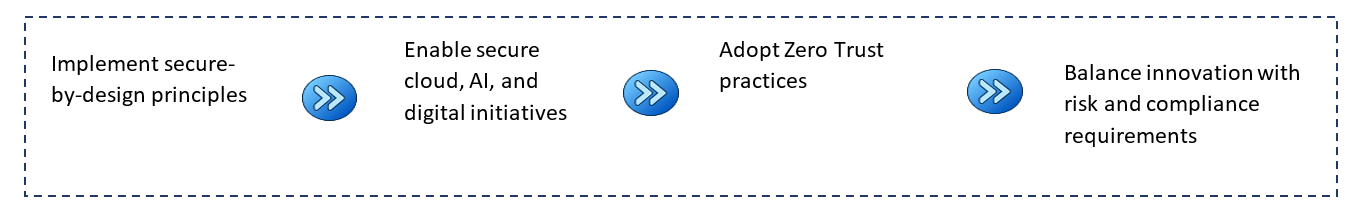
On the contrary, a secure environment is a launchpad for innovation. By eliminating uncertainty and providing guardrails, cybersecurity frees IT teams to experiment and deploy new solutions confidently. Real-world examples from fintech and digital health sectors demonstrate that organizations with strong security postures are quicker to adopt emerging technologies such as AI, blockchain, and IoT—without exposing themselves to undue risk.
How YASH can help
Conclusion and Actionable Takeaways for CIOs, CDOs, and CISOs
The evidence is clear: cybersecurity is no longer a box to check, but a strategic asset that can make or break M&A outcomes. By reframing security due diligence as a growth enabler, IT leaders can drive higher deal valuations, accelerate integration, and position their organizations for sustained innovation. As the digital landscape evolves, those who prioritize proactive, data-driven security will not only mitigate risk—they will define the future of M&A success.
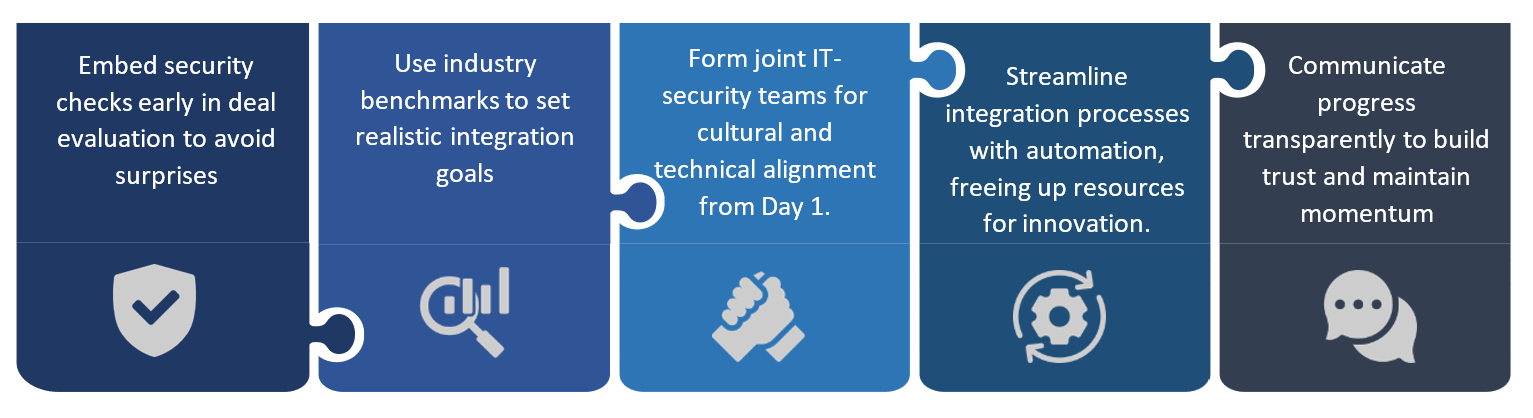
In the era of digital business, cybersecurity is not just a shield—it is a catalyst for growth. By embracing this mindset, CIOs, CDOs, and CISOs can transform security due diligence from a perceived obstacle into a decisive deal maker.
YASH Technologies: Ideal Due Diligence Partner
With 30+ years of IT expertise and a mature managed services portfolio, YASH Technologies helps organizations navigate Mergers, Acquisitions, and Divestitures seamlessly. From target identification and due diligence to integration and synergy track, we ensure smooth transitions and strategic focus.
For more details, visit our MA&D website.

More From Author.
Related Posts.


The Hidden ROI of Phase 0: Measuring What Never Happened
Akansha P Parimit Lohani
The Compounding Dollar Value
Gaurav Kankani Parimit Lohani
Beyond the Happy Path: How Asking the Right Questions During Discovery De-risks Automation
A V Shree Anurag Sameer Patnaik
Adapting to Inflation: The Necessity of Continuous Scenario Planning for a Sustainable Business
Prateek Goyal Sameer Patnaik